Sicurezza17 nov 20265 min
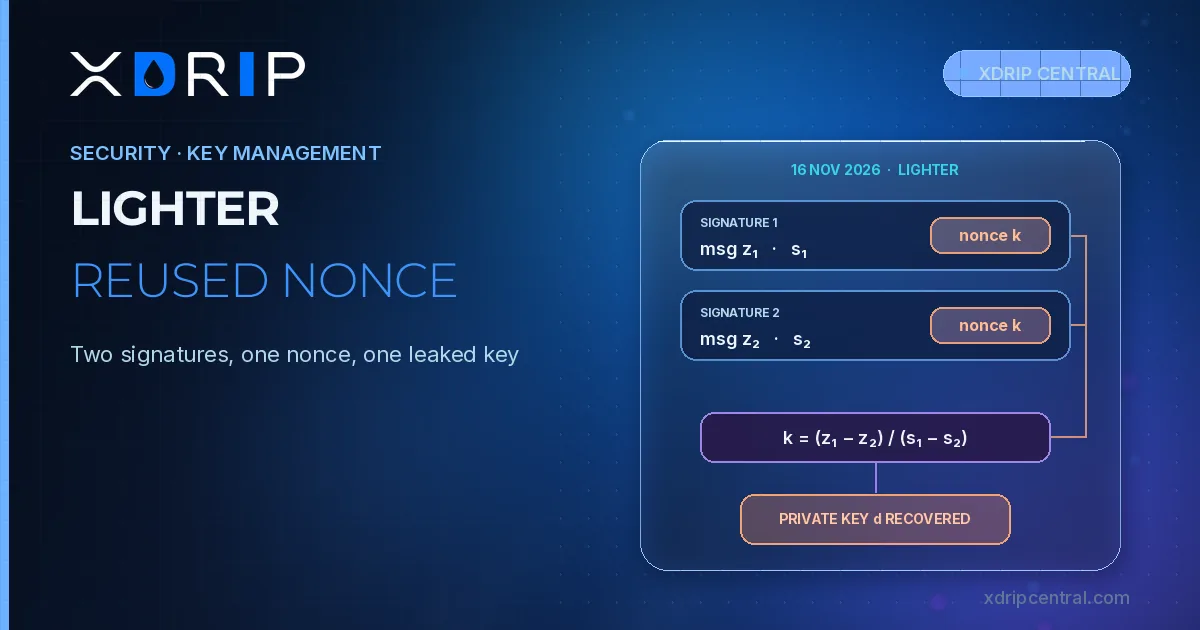
Lighter: How a Reused Nonce Leaked a Trader's API Key
About 10.39M USDC left Lighter after a trader's signing code reused nonces, exposing an API key. How the key leaked, how funds moved and what changed.
Sicurezza17 nov 20265 min
About 10.39M USDC left Lighter after a trader's signing code reused nonces, exposing an API key. How the key leaked, how funds moved and what changed.
Sicurezza11 nov 20264 min
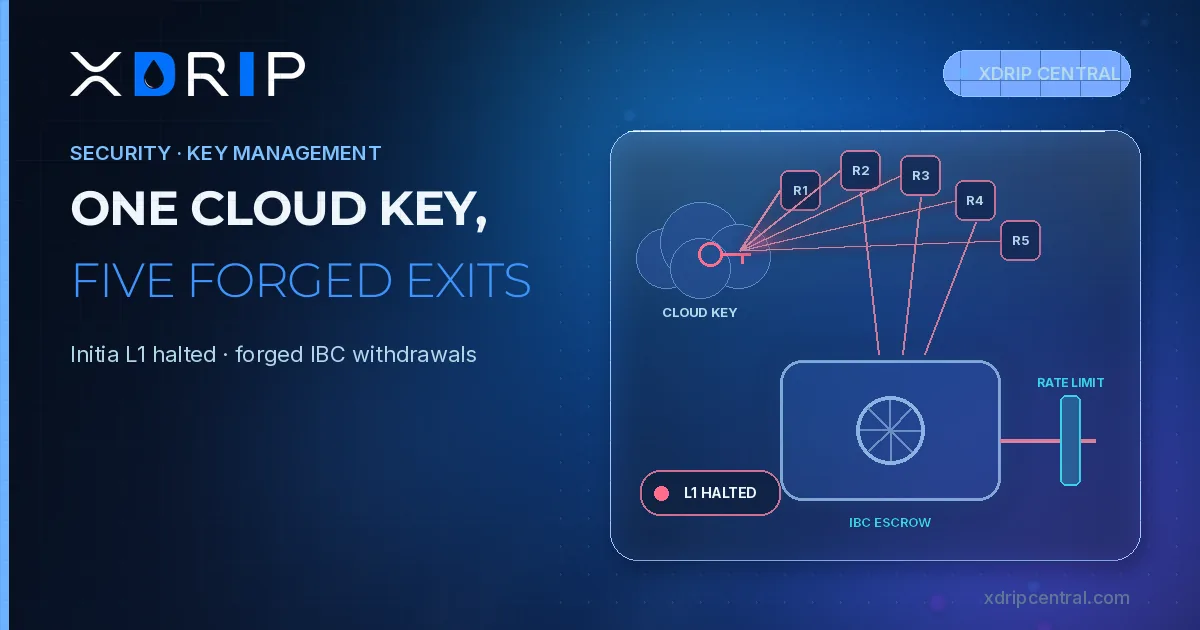
A leaked GCP key let an attacker forge IBC withdrawals from five Initia rollups and move $3.27M from L1 escrow. What happened, and what is still unknown.
Sicurezza10 nov 20264 min
Malicious bee-js 13.3.0 and Swarm Desktop 0.56.2 shipped through Swarm's own signed pipeline, targeting node wallet keys. What is known and unknown.
Sicurezza9 nov 20264 min
Web3Auth paused embedded wallets after a flaw exposed Keplr Google/Apple login keys. Millions moved to recovery addresses, not a theft total.
Sicurezza6 nov 20264 min
Chainalysis says password hashes and live tokens for all users were exposed. KYT went offline after abnormal activity. What the firm disclosed.
Sicurezza5 nov 20264 min
Crédit Mutuel Arkéa confirms an attack via a provider platform, with funds possibly converted to crypto. What the bank, Bitquery and the chain show so far.
Sicurezza4 nov 20264 min
Hot wallets on BTCPay Server 2.4.1 and earlier were swept from 1 Nov. Why updating is not enough, what we saw on-chain and what is still unknown.
Sicurezza3 nov 20265 min
Mercado Bitcoin wallets on 10+ chains were drained on 2 Nov. Estimates run from $38M to $49M, about $11M is frozen. What we verified on-chain and what is open.
Sicurezza2 nov 20264 min
A one-block Ethereum reorg on 31 Oct made THORChain pay out 10 ETH it never received. What we verified on-chain, what is still open, and the finality lesson.
Sicurezza30 ott 20265 min
An EIP-7702 delegation let an attacker sweep a Binance hot wallet on 29 Oct. What we verified on-chain, what is still open, and the signing lesson.
Sicurezza29 ott 20264 min
A Humanode EVM precompile flaw let an attacker spend existing allowances: 12.77M eHMND from 436 accounts, per the team. Fixed in 40 minutes.
Sicurezza28 ott 20265 min
A 2-of-7 Avalanche Safe approved an empty address in March. An MEV bot ran the drain first, then returned funds for a bounty. We checked it on-chain.